install Google-Authenticator app on whatever device you prefer
Then you do this on Ubuntu 11.10 (oneric):
git clone https://code.google.com/p/google-authenticator/
install libqrencode library
install libpam0g-dev
cd google-authenticator
sudo make install
run google-authenticator
Time-based tokens: Y
Scan the QR code you get up on screen with your authenticator app
Update .google-authenticator file: Y
Disallow use of same authentication token: Y
Increase window for time-skew: N
Rate-limiting: Y
insert auth required pam_google_authenticator-so into your /etc/pam.d/sshd file
sudo restart ssh
go.
Monday, April 23, 2012
Tuesday, April 10, 2012
Passwords^12 : Call for Presentations
 |
| [Still haven't asked anyone to make a logo...] |
CALL FOR PRESENTATIONS IS NOW CLOSED.
PRACTICAL INFO HERE.
For the third year running, I am happy to once again announce a Call for Presentations for Passwords^12.
Passwords^12 will be held at the University of Oslo (Norway) on December 3-5, 2012. The 2-day conference will be free and open for anyone to attend. Please do note that our primary audience will be academics and security professionals with deep technical knowledge. This is a conference with international speakers and participants, presenting fresh ideas and innovative research in an area that affects us all.
Saturday, April 07, 2012
Improving Password Meters
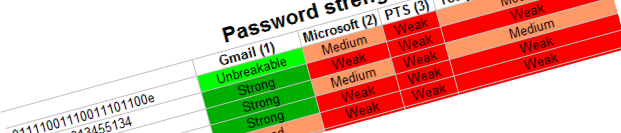
I've cried and cursed over password meters earlier. Twice actually. I've been planning to do it again too, just haven't found the time yet. (Volunteers?)
Then this site appeared in my Twitter stream - HowSecureIsMyPassword.Net, and I soon got in contact with Mark (@smallhadron). A bit of e-mails, broken promises from my side supplying some constructive criticism etc, and here I am. Sorry Mark, but finally I couldn't keep these ideas in my head any longer, so here you are. I still hope and believe this can be of interest to you, as well as anyone else considering making their own password metering software. :-)
Thursday, April 05, 2012
It all started with a hash
 |
| [ Lots of clipart available. I did my own this time. ] |
This is a "Thank you all!" blog post, that will also provide something useful. At least; I hope so.
Not long ago, I found myself involved in a penetration test against an episerver installation. Working with my security colleagues @jabjorkhaug and @KluZz, we got access to some password hashes and their respective salts. Unfortunately the hash and salt values didn't look like those shown in the episerver patch for JtR by Johannes Gumbel in 2008. And here our quest began.... :-)
Wednesday, March 28, 2012
Viktig oppdatering - Adobe Flash Player

Adobe har kommet med en kritisk oppdatering som anbefales installert snarest, da den fikser kritiske sikkerhetssvakheter, og kommer i tillegg med en opsjon for automatisk oppdatering.
På mer forståelig norsk: Det har kommet en viktig oppdatering til et lite tilleggsprogram på datamaskinen din som bør installeres så fort som mulig. Dette tilleggsprogrammet er det som gjør at du kan se f.eks. reklame og videoer på en lang rekke nettsider, og brukes nesten over alt. I denne oppdateringen er det også kommet en funksjon som gjør at du heretter ikke trenger å tenke mer på å oppdatere den manuelt; det vil skje automatisk og uten at du legger merke til det.
PS: på jobben din ordner antagelig IT-avdelingen dette for deg automatisk!
Her er steg-for-steg guiden for hvordan du installerer oppdateringen:
Friday, March 23, 2012
Note to self: Ubuntu 11.10x64 + Nvidia
Install Ubuntu 11.10 x64 with all updates
sudo apt-get install gnome-panel (Unity be gone!)
Logout and pick gnome on login
Add https://launchpad.net/~ubuntu-x-swat/+archive/x-updates to software sources
sudo apt-get update
enable Nvidia hardware driver in hardware drivers
reboot
Install Virtualbox 4.1.x (problems with the guide at virtualbox.org on adding repository)
Go cudaHashcat*, Multiforcer & John.
Restore normal room temperature.
Wednesday, March 14, 2012
BYOD - har du lest den lille skriften?

På et tidspunkt tilbake i tid satt jeg på en høgskole sammen med staute grønnkledde mennesker, og der leste jeg blant annet sikkerhetsloven og utvalgte høydepunkter fra straffeloven. Lesingen sluttet ikke der, og for å bruke et ofte brukt uttrykk: Djevelen ligger i detaljene.
Thursday, March 01, 2012
Pwnd. Again. And again.
 |
| [My colleague Jørgen, putting up his best smile after a successful PWN of me] |
Sunday, February 12, 2012
Activesync and FIPS 140-2 part 1
 |
| Perhaps the best Dilbert/Mordac ever...? |
Seriously, I've been doing some testing with Microsoft Activesync in order to find some common ground across iOS & Android for setting a "good practice" password policy level. After spending some time on this, I think Mordacs work at Apple & Google. I also think that Mordac was involved in the creation of FIPS 140-2, at least when somebody thought it would be a good idea for mobile devices.
I'll explain that later on, but first 2 simple things to remember here:
1. A default policy, no matter which product, should never be considered "secure" or "good enough".
2. I say Good Practice. "Best practice" cannot be proven legally, period. There is a legal difference here.
Monday, February 06, 2012
STARTTLS & the Police
 |
| [Kids say the darndest things...] |
Subscribe to:
Posts (Atom)